On Monday, the security manager reviews the company risk register. Two days later, a developer modifies a cloud access policy. On Friday, someone uploads a revised security procedure, yet the Statement of Applicability still points to the earlier version.
Nothing especially alarming has happened. When an ISO 27001 auditor reviews the records, even small inconsistencies can become difficult to explain. Startups often struggle less with any single task than with keeping compliance work coordinated alongside daily operations.
When Managing Spreadsheets Becomes Another Job
Spreadsheets are widely understood, low-cost, and flexible. That convenience comes with risks: files can be left outdated or simply forgotten. At first, a small business might separate its risk register from policy and control records. That arrangement can work while the project is relatively simple, but problems appear when responsibilities shift or several employees make independent updates.
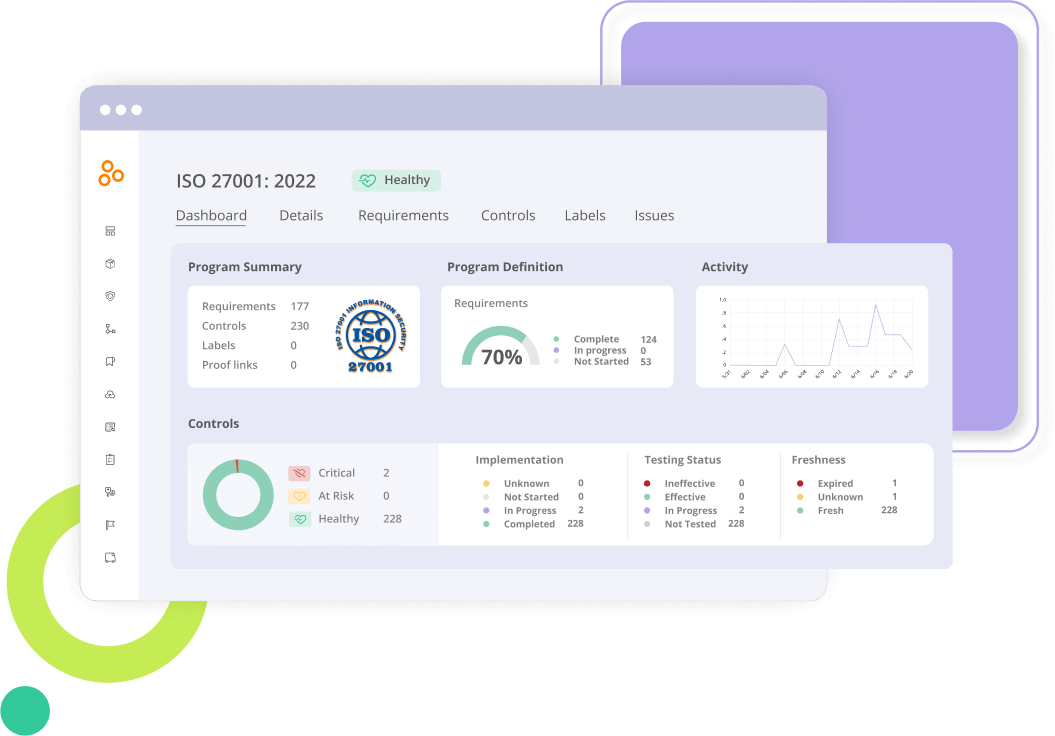
ISO 27001 compliance software offers an alternative by bringing related activities into a structured workspace. Instead of opening several spreadsheets to understand a control’s status, team members can find its documentation and supporting evidence together.
Before You Subscribe, Consider Who Owns the Work
Before committing to a platform, founders should consider who will maintain it.
An eight-employee startup may need a less elaborate system than a large multinational organization. Founders may handle risk assessments, developers may maintain technical controls, and an operations manager may organize documentation.
The right ISO 27001 software should clarify these responsibilities without adding complicated administrative tasks. If employees are reluctant to update a system, its capabilities are unlikely to deliver much practical benefit.
The Statement of Applicability Needs Accurate Records
A Statement of Applicability should be treated as an important record of control decisions. It explains which security controls an organization considers necessary, why those controls were selected, and whether they have been put into practice.
For example, a company using cloud-hosted infrastructure still needs to consider relevant physical security risks, even when the cloud provider handles the physical infrastructure.
The organization’s responsibilities and control decisions should be kept up to date. A connected risk register and Statement of Applicability can make those decisions more straightforward to demonstrate during an audit.
Preparing for the ISO 27001 Assessment
An auditor may ask to examine access management records, employee training evidence, security policies, or risk treatment decisions. Finding the latest approved documents becomes unnecessarily slow when records are spread across several systems. Although ISO 27001 certification software can bring evidence together, it cannot guarantee the evidence meets the requirements.
Whether the information security management system meets the standard is evaluated by an accredited certification body. Clear records simply make the assessment process easier to manage.
Choosing Practical Software for a Growing Business
A growing team should compare compliance platforms against its financial and operational constraints. CertAssist offers a straightforward option for businesses searching for the best compliance software for startups ISO 27001 certification. The platform includes ISO 27001 clauses, Annex A controls, a risk register, a Statement of Applicability, editable policy guidance, and evidence storage.
Auditors can be given direct access, and the platform does not require infrastructure integrations. That can be particularly useful for businesses that prefer managing evidence themselves.
How to Avoid Letting Compliance Slow Operations
A startup still needs to serve customers and build its product while preparing for certification; compliance work should not bring operations to a halt. A practical compliance system makes it easier to identify unfinished work, maintain accurate records, and prepare for independent assessment.
CertAssist is designed around that principle: giving smaller teams the structure needed to manage ISO 27001 without building an unnecessarily complicated compliance operation. A long feature list is not, by itself, proof of usefulness. What matters is whether your team can keep its security responsibilities manageable as the business grows.